

The Paraluni project was attacked on the morning of March 13 (UTC +8 time). The attacker leveraged two vulnerabilities to attack the protocol. The first vulnerability is the lack of the verification of passed tokens, and the second is the traditional reentrancy. The attacker launched a couple of attack transactions. In the following, we will use one of them 0xf2bba649019ce40a67f0fb74e5e800257d359d9094b6ba6faea14ffa4d3446b1 to illustrate the whole attack process.
Step I: add liquidity to paraRouter
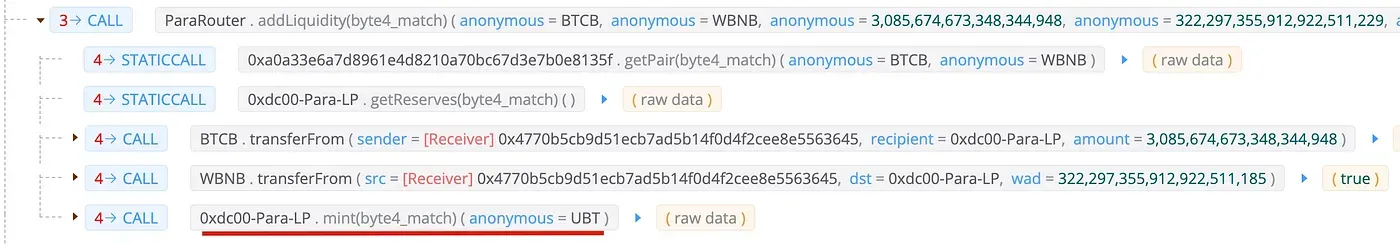
The attacker invoked addLiquidity to the BTCB-WBNB pool (index = 9) and the pool will mint the lp token to UBT (a token created by the attacker.) After this operation, the UBT token holds the pool's lp token. Note that, the BTCB and WBNB is borrowed from the flash loan.
Step II: invoke depositByAddLiquidity of MasterChef
The attacker invoked depositByAddLiquidity by providing the _pid as 9 and using the UGT and UBT token as the parameters. However, the function does not check whether the pool’s reserve tokens are equal to the passed tokens (UGT and UBT).
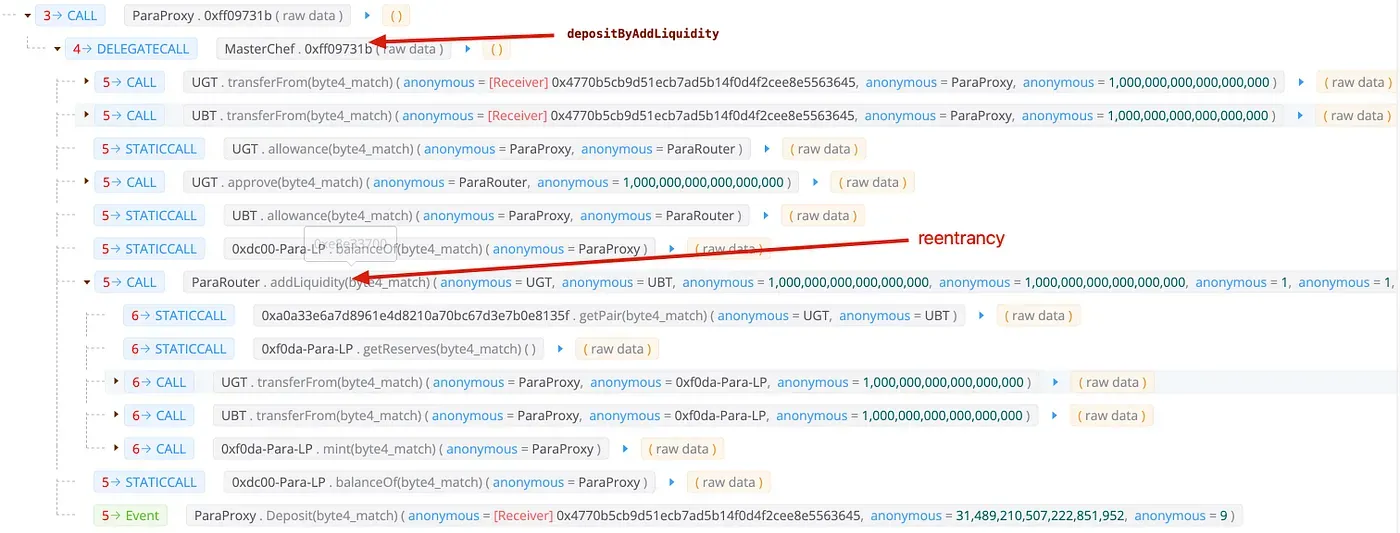
Then the function invokes the depositByAddLiquidityInternal which then invokes addLiquidity of paraRouter. This function will invoke the UGT and UBT token’s transferFrom function. However, these two tokens are controlled by the attacker. In the transferFrom function of UBT, the attacker invoked deposit function of the MasterChef contract to deposit the LP token obtained in the first step into MasterChef contract.
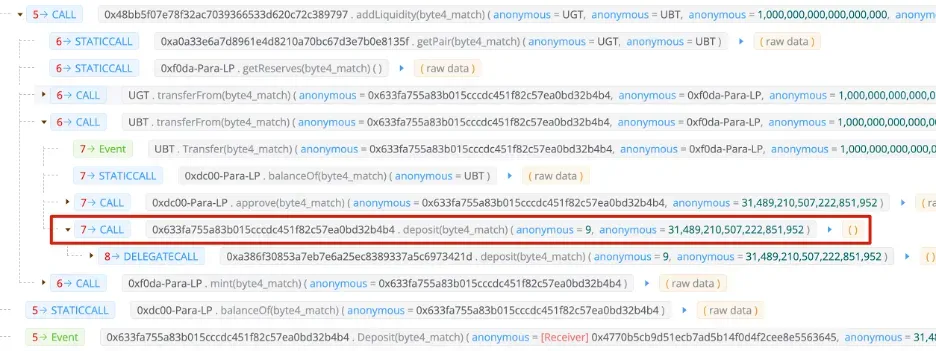
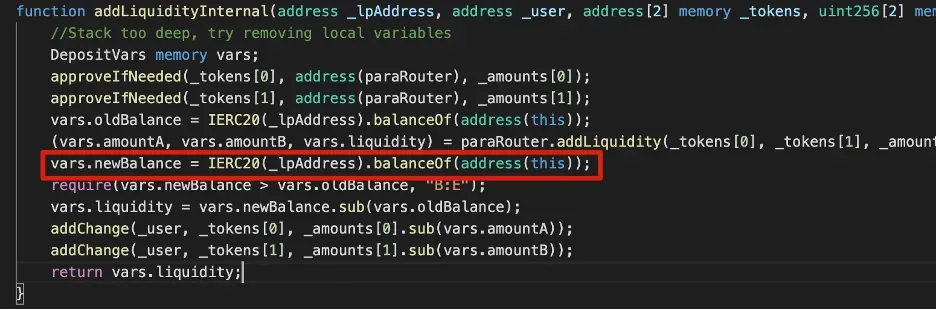
Unfortunately, due to the balance change in the deposit function, the newBalance after addLiquidity is much larger than the oldBalance. In this way, the attacker got double credits in MasterChef contract.
Step III: get profit
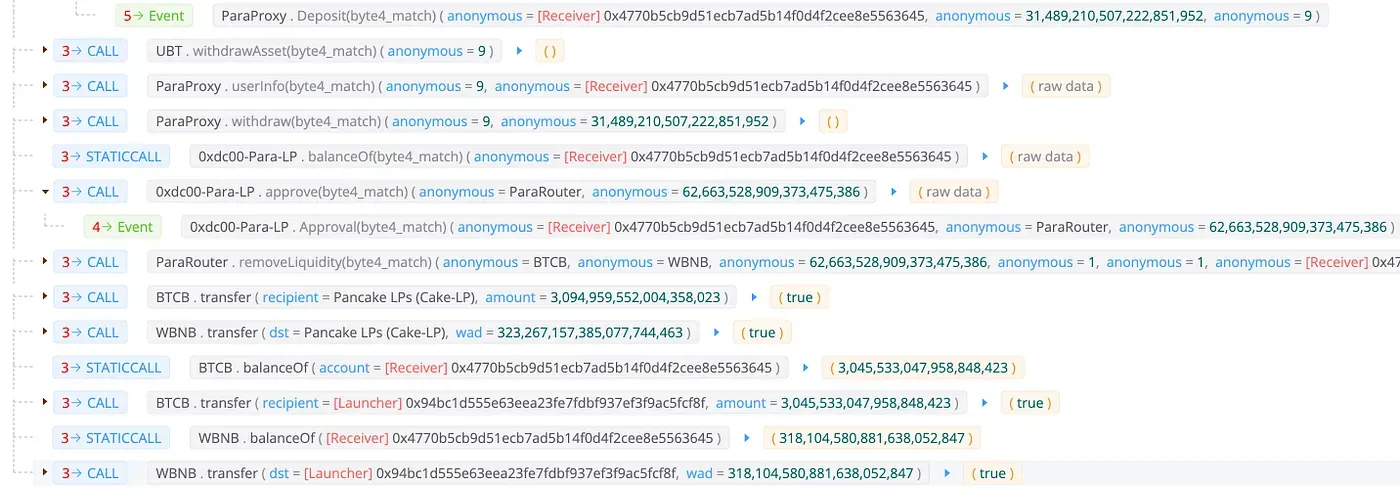
The attacker finally invoked UBT.withdrawAsset and MasterChef.withdraw to redeem the lptoken to get BTCB and WBNB. Since the number of liquidity is more than the attacker should have, the attacker will get profits.
Lessons
Besides the reentrancy problem, the passed tokens have not been verified is one of the root causes. We have seen other cases with similar issue, as in the Visor case and the Coin98 case.
About BlockSec
BlockSec is a pioneering blockchain security company established in 2021 by a group of globally distinguished security experts. The company is committed to enhancing security and usability for the emerging Web3 world in order to facilitate its mass adoption. To this end, BlockSec provides smart contract and EVM chain security auditing services, the Phalcon platform for security development and blocking threats proactively, the MetaSleuth platform for fund tracking and investigation, and MetaSuites extension for web3 builders surfing efficiently in the crypto world.
To date, the company has served over 300 esteemed clients such as MetaMask, Uniswap Foundation, Compound, Forta, and PancakeSwap, and received tens of millions of US dollars in two rounds of financing from preeminent investors, including Matrix Partners, Vitalbridge Capital, and Fenbushi Capital.
Official website: https://blocksec.com/
Official Twitter account: https://twitter.com/BlockSecTeam



